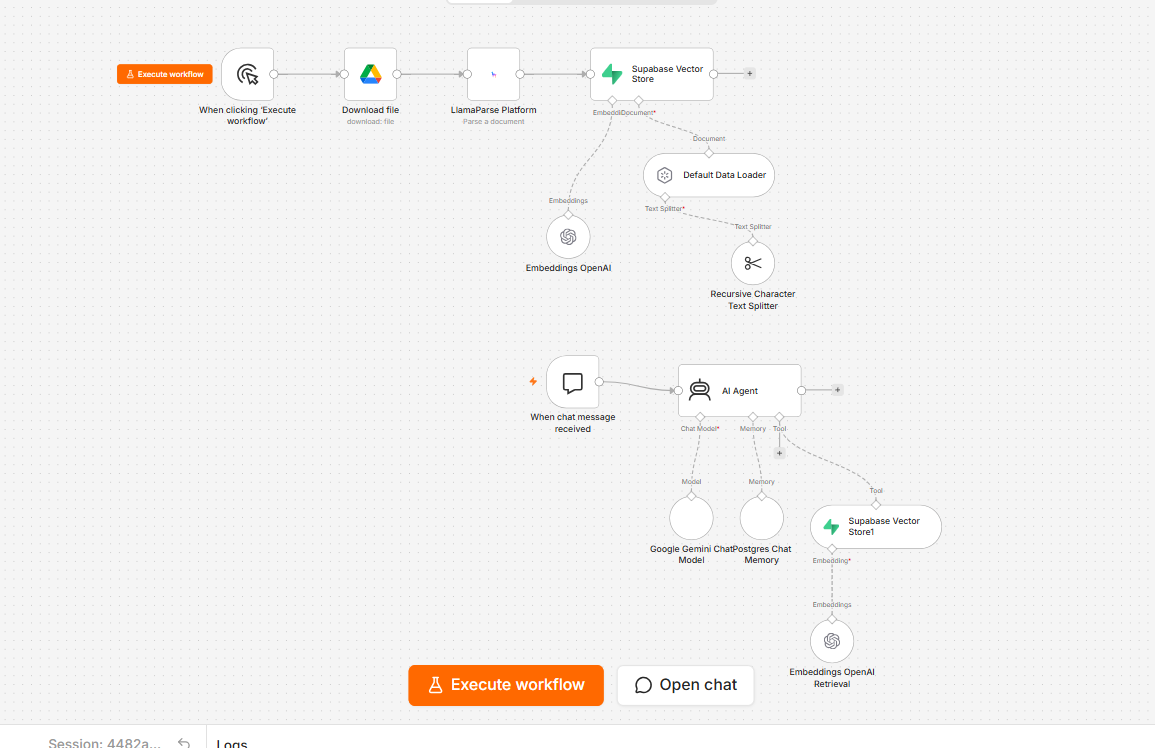
Permission-Aware RAG Agent
Tech Stack
The Problem
Standard RAG setups retrieve all semantically relevant chunks first and rely on LLM system prompts to filter sensitive data. When adversarial users use indirect prompt injection, the LLM can easily be manipulated into leaking confidential corporate records, financial numbers, and executive strategy.
The Result
Enforced deterministic pre-retrieval Role-Based Access Control directly inside PostgreSQL/pgvector using a custom match_documents_rbac stored procedure. Documents are filtered at the database layer (WHERE clearance = ANY(allowed_tiers)) before vector distance scoring occurs, ensuring unauthorized chunks never enter the LLM context window with mathematical immunity against context leaks.
Direct Inquiries & Strategy Sessions
Ready to build custom AI agents, automated workflows, or enterprise data pipelines? Reach out directly via: